The ELISA Project community gathered at Canonical’s London office from June 9–11, 2026, for three days of technical presentations, discussions, and collaboration focused on advancing Linux for safety-critical applications.
The workshop included discussions on regulatory approaches to AI-based tooling, the role of software preservation and identification in supporting assessment evidence, and ongoing work to improve Linux kernel test coverage. The main topics included emerging standards, requirements-to-test-to-code traceability, long-term access to source code, fault injection, and challenges in testing kernel drivers.
In this blog from our post-event series, we highlight three sessions covering these topics. The first compared approaches to AI-based tooling across automotive, industrial, and aerospace markets, concluding with a proposal to bring standards expertise and practical pilot projects together through the ELISA Tools Working Group. The second explored how Software Heritage and Software Hash Identifiers can connect best practices and assessment evidence to exact software artifacts that remain identifiable and retrievable over time. The third presented stress-ng’s expanding tests, the use of coverage analysis to identify untested code paths, and plans to improve coverage of common driver code with input from the ELISA community.
Facilitated feedback and discussion and comparison of market’s views of AI based tooling – Olivier Charrier, Wind River
Olivier Charrier of Wind River led a discussion on AI-based tooling in safety-related development, comparing regulatory approaches across automotive, industrial, and aerospace markets. The session explored emerging standards, the influence of the EU AI Act, and proposed limitations on the safety assurance credit available for different types of AI tools in avionics. Olivier emphasized the importance of understanding the regulatory requirements of the intended market, engaging with auditors early, and following standards discussions to guide tool selection and development processes.
Workshop attendees also discussed the value of understanding the rationale behind standards and sharing insights across industries to make approaches more reusable. The session concluded with a proposal to bring standards expertise and practical experimentation together through the ELISA Tools Working Group, using a small number of pilot projects and open source proofs of concept to explore AI adoption in safety-related development. Slides here.
From Best Practices to Evidence: How SWH and SWHID Support Trustworthy Open Source – Wendi Urribarri, Woven by Toyota
Wendi Urribarri of Woven by Toyota explained how Software Heritage and Software Hash Identifiers (SWHIDs) can support trustworthy open source by connecting best practices, assessment evidence, and exact software artifacts. She distinguished SWHIDs, which identify artifacts by their content and can be used independently, from Software Heritage, which preserves source code and its history. The session emphasized the need to identify what was assessed, reviewed, or reused and to retrieve that same code years later, even if repositories move or disappear.
Examples showed how SWHIDs can complement package URLs and SBOM metadata, and support traceability from requirements and tests to specific source files or lines. Urribarri connected this approach to assessment initiatives including Lighthouse OSS, OpenSSF Best Practices, and Trustable. Participants also discussed linking source code, build configurations, toolchains, and binaries to support reproducibility, as well as retrieving exact historical code for targeted fixes and reassessment. Slides here.
Improving kernel test coverage with stress-ng – Colin King, stress-ng maintainer
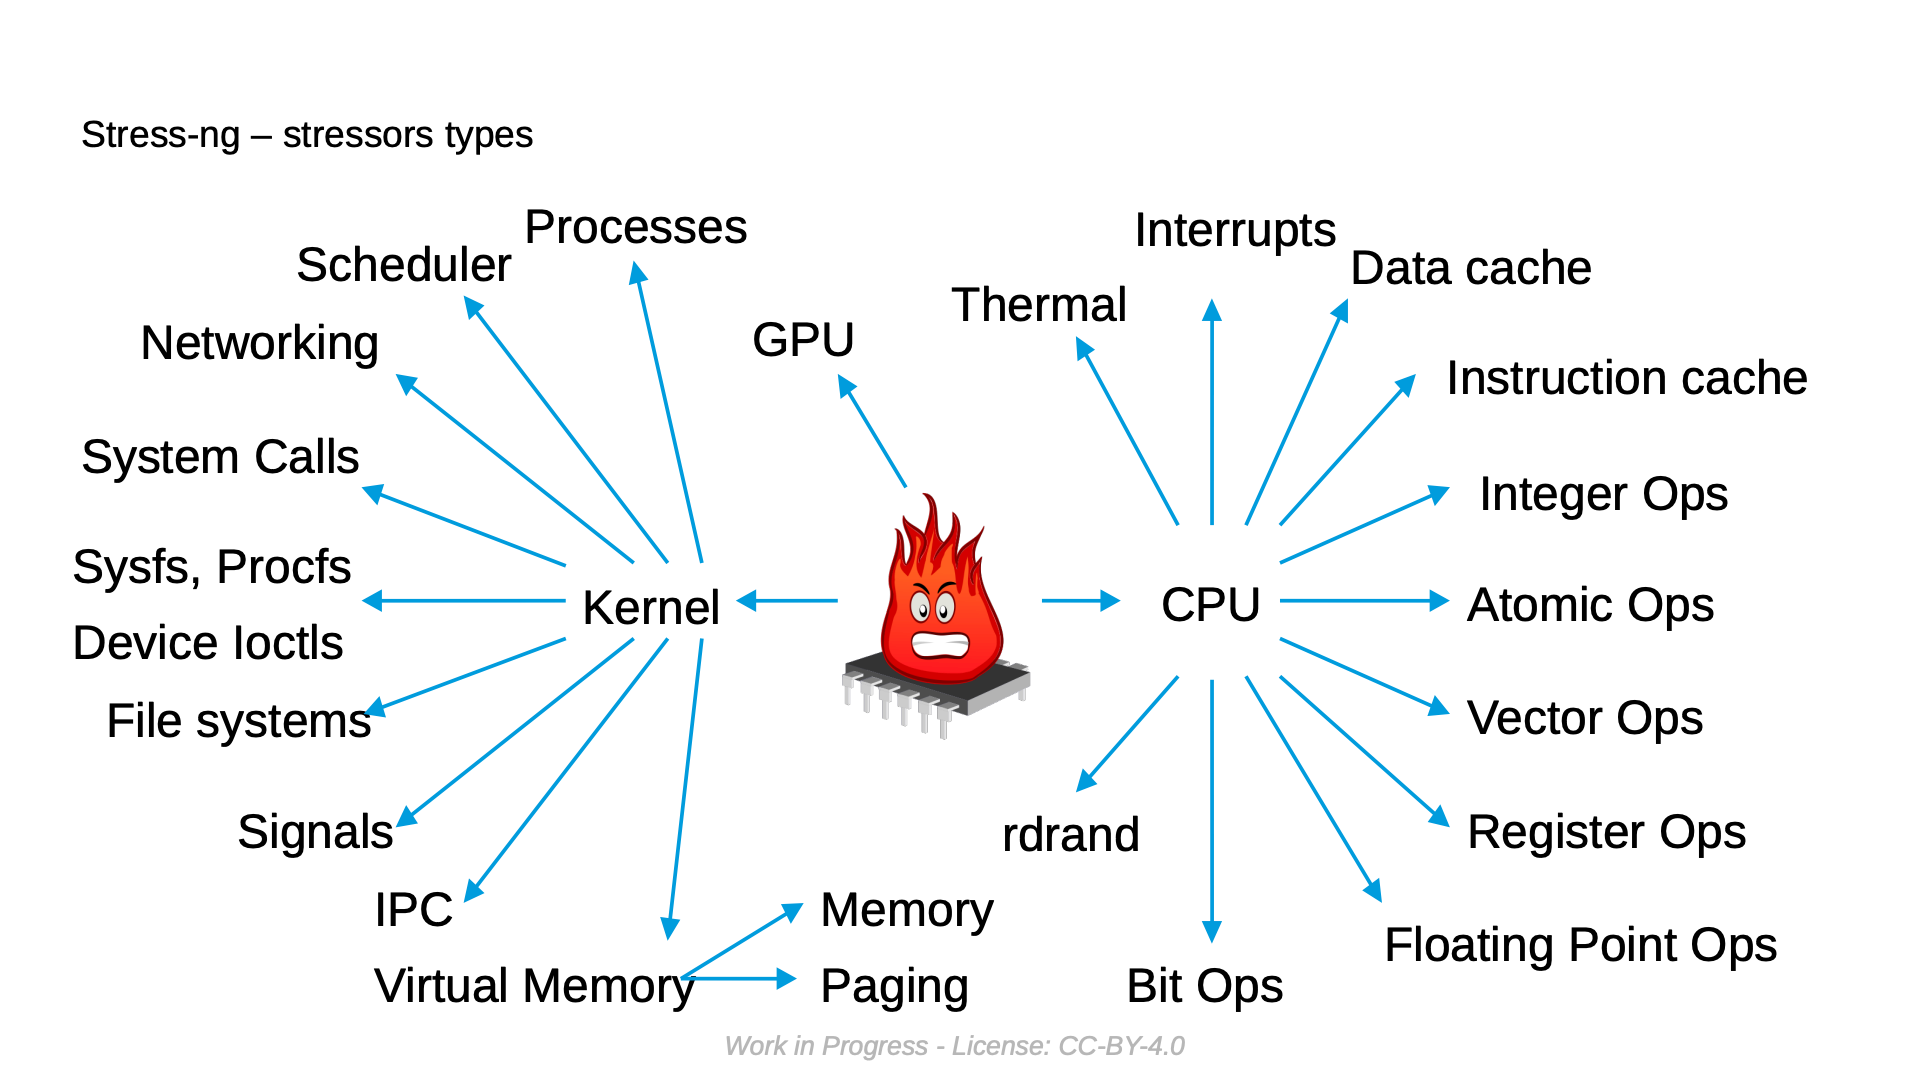
Colin King, maintainer of stress-ng, presented ongoing work to improve Linux kernel test coverage by exercising system calls and kernel interfaces. He described new stressors for scheduling, filesystems, memory, and networking, including tests targeting race conditions, read-only filesystems, and invalid file descriptor operations. Using gcov and lcov, Colin showed how coverage analysis reveals missing test cases and untested error paths. He also explained how fault injection can trigger memory allocation failures to exercise error handling, and shared examples of bugs uncovered through stress testing.
Colin highlighted that although stress-ng’s coverage is increasing, the kernel is growing faster than his testing can keep up, with major gaps in driver coverage. He outlined plans to target common driver code and develop generic tests, inviting the ELISA community to identify priority drivers and provide access to relevant hardware. The discussion also raised opportunities to document the interfaces exercised by each stressor and collaborate on tool classification and qualification for safety-related use. Slides here.
These sessions explored regulatory considerations for AI-based tooling, the preservation and identification of software artifacts supporting assessment evidence, and improvements to Linux kernel test coverage. Together, they emphasized understanding the requirements of the intended market, keeping assessed software identifiable and retrievable over time, and using coverage analysis to identify untested code paths.
The discussions also raised proposals for further collaboration, including combining standards expertise with AI pilot projects through the ELISA Tools Working Group, identifying priority drivers and providing hardware for stress-ng testing, and working together on tool classification and qualification for safety-related use.