THE LINUX FOUNDATION PROJECTS
Category

Blog

Join the ELISA Project at Open Source Summit Korea 2026

Join the ELISA Project at Open Source Summit Korea 2026

By Announcement, Blog, Critical Software Summit, Industry Conference, Safety-Critical Software Summit

How can open source software meet the rigorous requirements of safety-critical systems? What role can AI, memory-safe technologies, traceability frameworks, and real-time security play in building systems that are both open and dependable?

These questions will be discussed at Open Source Summit Korea 2026, taking place on August 11–12. The event brings together developers, maintainers, technologists, community leaders, and open source professionals from across the ecosystem to share knowledge, collaborate on solutions, and discuss emerging technologies.

With sessions covering cloud infrastructure, Linux, AI and machine learning, embedded systems, security, governance, legal topics, and community strategy, Open Source Summit provides a cross-domain space where technical and non-technical contributors can connect and learn from one another.

The ELISA Project will also be part of the Safety-Critical Software track. This track focuses on the intersection of open source software and safety standards, including regulatory compliance, security updates, requirements traceability, quality assessments, safety analysis methodologies, and the technical development of safety-critical systems.

Don’t forget to add these sessions to your schedule!

Tuesday August 11, 2026 11:00 – 11:30 KST – Sponsored Session: A New Security Standard for the AI Era: Zero-CVE and Real-Time Threat Response – SeungEll Lee, Red Hat

As Generative AI and Agentic AI continue to evolve, cyberattacks have become increasingly automated. With hundreds of new CVEs disclosed every day and AI-powered attacks automated in zero-hour, traditional security and patch management approaches have reached their limits.

This session explores how organizations can build a lightweight hardened infrastructure and a trusted Zero-CVE environment with Red Hat AI on a proven platform that leverages the strengths of the open source ecosystem. It also examines the need for autonomous defense systems and approaches to implementing them, enabling real-time threat response while maintaining infrastructure stability through controlled AI-driven automation.

Breaking the Sharing Paradox: A Working Foundation and a Call for the Next Phase – Jinyong (Dave) Jeon, SOOHO

Institutional blockchain systems need collective defense, yet the data behind the vulnerabilities they discover cannot leave the institution. The OpenReagent project was launched to break that paradox through an open standard built on sharing signatures, not source. A year in, the concept has become a working technical foundation, with early benchmark evidence and first conversations with institutions testing real fit. This session shares what that foundation now enables, and what it doesn’t yet, and issues a direct call to researchers ready to deepen the technical frontier, and to institutions ready to join the initiative as early partners.

Wednesday August 12, 2026 15:55 – 16:25 KST – Case Studies of Existing Use of Linux in Safety-critical Domains – Nikita Verma, Individual & Harshita Varma, Independent

The automotive transition to Software-Defined Vehicles (SDVs) relies on mixed-criticality architectures, consolidating open-source infotainment (Automotive Grade Linux) alongside safety-critical Real-Time Operating Systems (RTOS). This virtualization boundary—often KVM/Xen—is assumed to be a secure airgap. However, guest-to-host communication requires hardware abstraction, primarily via the VirtIO standard.

This 40-minute session conducts a hardcore technical teardown of the virtqueue shared-memory mechanism, exposing how legacy C-based VirtIO backends (vhost-net) introduce critical vulnerabilities into the automotive supply chain.

The speakers will dissect a hypervisor escape utilizing custom fuzzing. By crafting malformed descriptor chains to bypass frontend validation, a compromised guest can force the host’s backend into out-of-bounds memory corruption, effectively bridging the airgap into the control plane.

Finally, the speakers will architect the open-source defense: migrating to memory-safe rust-vmm virtualization components to mathematically eliminate buffer overflows, and deploying zero-overhead eBPF probes for kernel-level I/O anomaly detection.

Wednesday August 12, 2026 16:35 – 17:05 KST – Using AI To Bridge the Gap Between Safety Standards and Open Source Development – Kate Stewart, The Linux Foundation

Popular open source operating systems like the Linux Kernel and Zephyr RTOS accept up to 9 commits per hour. Safety standards, like 61508, 26262, and others were developed without this rate of change in mind. Safety standards also expect the requirements to be explicit, which is not part of OS development processes. By using AI tools, we’re able to accelerate the analysis of OS code to derive the requirements and traceability to tests. By storing this info in tools that can import and export System Package Data eXchange (SPDX) 3.0+, we’re able to capture the requirements in a way that can be leveraged for wider system analysis necessary for safety. Associating integrity methods with the requirements and code snippets, also enables monitoring. Combining requirements traceability with precise build SBOM metadata, gives us a framework to keep a component compliant to a safety profile after a security fix.

This talk will provide a view on the latest experiments occurring with the Linux Kernel in the ELISA project, as well as in the Zephyr Safety Working group, and SPDX Functional Safety working group to extend SPDX to meet the needs of establishing these frameworks.

Join the Conversation

As open source software becomes increasingly important in automotive, industrial, medical, and other safety-critical environments, collaboration across projects, companies, standards organizations, and technical communities is essential.

The Safety-Critical Software track offers an opportunity to learn how the open source community is addressing security, compliance, traceability, virtualization, AI-assisted analysis, and long-term software maintenance. Join the ELISA Project and the wider open source community at Open Source Summit Korea 2026 to learn about the technologies, practices, and partnerships helping move safety-critical open source development forward.

Learn more about the event and register here.
Welcome, Ritsumeikan University! (1)

Ritsumeikan University Joins the ELISA Project!

By Announcement, Blog

We are thrilled to announce that Ritsumeikan University has officially joined the ELISA Project as an Associate Member!

As an open source initiative dedicated to defining and maintaining a common set of tools and processes to help companies build and certify Linux-based safety-critical systems, expanding our academic partnerships is vital..

Who is Ritsumeikan University?

Founded in Kyoto, Japan, Ritsumeikan University is a highly respected, comprehensive private university renowned for its commitment to cutting-edge research, international collaboration, and technological innovation. With its heavy focus on next-generation scientific advancement, Ritsumeikan has established itself as a premier institution for engineering and information science in Asia and beyond.

The Expertise They Bring to ELISA

While welcoming a new member is always an exciting step, it is Ritsumeikan’s deep well of research expertise that makes this partnership so impactful for the future of safety-critical Linux. Here is a closer look at the technical strengths they bring to the table:

  • Information Science & Systems Architecture: Ritsumeikan’s College of Information Science and Engineering is a recognized leader in embedded computing, operating system analysis, and dependable computing. Their researchers actively explore how to make complex software environments more robust, secure, and resilient – a mission that perfectly aligns with ELISA’s core goals.
  • Real-Time Data & IoT: From IoT systems, cyber-physical systems, and secure distributed infrastructures to edge computing platforms, Ritsumeikan is constantly pushing the boundaries of how data is processed on the fly. This hands-on experience with real-time data handling is invaluable for safety-critical systems, where latency and reliability can be a matter of life or death.
  • Automotive & Mobility Systems: With Japan being a global hub for automotive engineering, Ritsumeikan has fostered deep ties with the mobility sector. Their advanced research into dependable control systems, connected mobility platforms, intelligent transportation systems, and safety assurance methodologies provides vital academic insights that will greatly benefit the automotive and aerospace working groups within ELISA.
  • Cybersecurity for Safety-Critical Systems: Ritsumeikan researchers actively investigate cybersecurity for embedded and distributed systems, including IoT device protection, threat analysis, network security, and attack monitoring. As software-defined systems become increasingly connected, ensuring both safety and security is essential for certification and deployment.
  • A Holistic Approach to Safety: Ritsumeikan uniquely bridges the gap between hardware engineering, software development, and the Ethical, Legal, and Social Implications (ELSI) of new technologies. This interdisciplinary approach ensures that system safety isn’t just treated as a coding hurdle, but as a comprehensive societal priority.

Looking Ahead

Certifying Linux for safety-critical applications – whether for medical devices, industrial robotics, railways, or autonomous vehicles – requires both industry experience and academic research. By welcoming Ritsumeikan University, we are expanding our global reach and adding a formidable research partner to our ranks.

Please join us in welcoming Ritsumeikan University to the ELISA Project!

ELISA Resources

Stay connected and get involved with our growing community through the following channels:

  • Discord: Join the real-time conversation with developers, researchers, and working groups on the ELISA Project Discord.
  • LinkedIn: Follow the ELISA Project LinkedIn Page for professional updates, event announcements, and networking.
  • Newsletter & Mailing Lists: Sign up for project updates and technical discussions via the ELISA Mailing Lists to get the latest news delivered straight to your inbox.
Blog - The Final Phase of Xen Safety: Solving Coverage and Residual Gaps - Stefano Stabellini, AMD

The Final Phase of Xen Safety: Solving Coverage and Residual Gaps – Stefano Stabellini, AMD

By Blog, Critical Software Summit, Safety-Critical Software Summit

Open Source Summit North America 2026 and Embedded Linux Conference brought together the open source community in Minneapolis from May 18–20, 2026.

For the ELISA Project community, the event was an important opportunity to continue the conversation around safety-critical software, open source safety standards, regulatory compliance, requirements traceability, verification, software supply chains, and safety engineering.

The Safety-Critical Software Track highlighted practical work across several domains, including aerospace, embedded systems, medical devices, robotics, avionics, automotive, and industrial systems. Sessions explored how open source communities are addressing the technical, process, and compliance needs of safety-critical systems.

Over the next few weeks, we will highlight selected session recordings from the track and share key takeaways with the community.

This week, we highlight “The Final Phase of Xen Safety: Solving Coverage and Residual Gaps,” presented by Stefano Stabellini, AMD.

Moving Xen Toward Final Safety Certification

AMD, in collaboration with the Xen community, is working to make the Xen hypervisor safety-certifiable to ISO 26262 ASIL D and IEC 61508 SIL 3 on Arm and AMD x86 platforms.

Stefano explained that the first phase of the project, Safety Concept Approval, has been completed. During this phase, safety assessors reviewed the project plans and examples of the safety artifacts.

The team is now nearing completion of the second phase, which focuses on carrying out those plans and addressing the remaining gaps in the certification effort.

The work is being developed in collaboration with the upstream Xen community rather than through a private fork. Major changes have been upstreamed, the Xen branch being prepared for certification is publicly available, and the team is working to make requirements, examples, tools, and infrastructure public wherever possible.

Xen’s Role in Functional Safety

Xen’s role in a functional safety system is to enforce isolation and freedom from interference between virtual machines.

This means ensuring that one virtual machine cannot affect another through memory access, security issues, latency, performance, or other system resources.

The session reviewed how Xen’s architecture can support embedded and safety-critical systems. Traditional Xen deployments often rely on Dom0, a large and highly privileged domain used to start and manage other virtual machines.

In embedded systems, the required virtual machines are often known before the platform starts. Xen can therefore launch them directly at boot, reducing the need for a large and privileged Dom0 environment.

Stefano described a model that separates responsibilities between a small control domain and a hardware domain. The control domain can monitor and restart selected virtual machines, while the hardware domain can manage devices and drivers without receiving unnecessary privileges.

Xen can also support untargetable domains that cannot be controlled or monitored by other domains. These domains can be used for safety-related workloads that require stronger isolation.

The Challenge of Complete Code Coverage

A central focus of the presentation was one of the most difficult remaining challenges: achieving complete code coverage.

Stefano explained that safety verification requires teams to document the behavior of the software and test that behavior. The combined test results must cover the code included in the certified software, including the independent conditions required for Modified Condition/Decision Coverage, or MC/DC.

This is particularly difficult for an open source project such as Xen.

Xen supports many processor vendors, platforms, configurations, and use cases. However, a specific certified configuration may only use a limited subset of this functionality.

For every code path, the team must therefore either test it or remove it from the final binary.

Removing Unused Code

Xen already uses Kconfig to enable and disable features before compilation. However, this is not sufficiently granular to remove every code path that falls outside a specific safety configuration.

Adding large numbers of conditional compilation statements would also make the upstream code more difficult to maintain.

Instead, the team is using compiler dead-code elimination.

By giving the compiler enough information about the selected configuration, code paths that cannot be reached can be removed automatically from the final binary.

One example involved processor-vendor-specific code. In a configuration that supports only AMD processors, the compiler can remove switch cases for other processor vendors.

Another example involved Xen’s x86 instruction-decoding code. Older x86 systems required Xen to decode trapped guest instructions manually. Modern systems provide more information about the instruction that caused the trap, so many legacy decoding paths are not required.

By limiting the configuration to modern hardware, the compiler can remove those unused paths.

Stefano showed how small source-code changes can allow the compiler to remove large sections of unused code without adding extensive conditional statements throughout the source.

The linker’s garbage-collection functionality can then remove entire functions that are no longer called.

Aligning Coverage Data With the Binary

Removing functions during linking creates an additional coverage challenge. Coverage notes are generated during compilation, but linker garbage collection happens later. As a result, the coverage information may still contain functions that were removed from the final binary.

Those functions could incorrectly appear as uncovered. To address this, the team developed two Python tools.

The first tool analyzes linker information, including the build log, map file, linker output, and DWARF data, to identify functions that were removed. It then creates a plain-text configuration showing which function was removed from which object file.

The second tool uses this information to remove the corresponding entries from the compiler-generated coverage notes. This process also accounts for static inline functions, which may be removed from one object file while remaining present in another.

The result is coverage information that more accurately represents the code included in the final binary.

Automating Fault Injection With QEMU

The session also covered fault injection, which is required to test how the software handles hardware errors.

Traditionally, this work may involve physical hardware and hardware debuggers, making tests difficult to automate and repeat. The team is instead using QEMU so that fault-injection tests can be included in continuous integration workflows.

Stefano described a Python framework that interacts with QEMU through QMP, QTest, and GDB.

QMP can inject events such as non-maskable interrupts and machine-check exceptions. QTest can simulate memory-mapped input/output and I/O port operations. GDB can set breakpoints and modify memory, registers, stacks, and function parameters.

By combining these interfaces, the team can trigger specific Xen error-handling paths and test them without changing the Xen source code for each case.

This makes the tests automated, repeatable, and suitable for use in verification pipelines.

Working With the Open Source Community

Stefano emphasized that the effort is not limited to AMD. Several organizations are contributing to work around Xen and safety, with collaboration taking place in the upstream community.

The goal is not to certify a private fork and leave it unchanged. Instead, the project aims to improve the upstream Xen codebase and make certification easier to maintain and repeat over time.

Making requirements, tools, artifacts, and infrastructure publicly available can also help support different configurations and safety targets in the future.

The session provided a practical look at the remaining work in Xen’s safety-certification effort, including complete code coverage, maintainable code reduction, accurate coverage reporting, automated fault injection, and open source collaboration.

Watch the session recording here.

Stay tuned for more Safety-Critical Software Track session highlights from Open Source Summit North America 2026. Check the playlist here.

Clip - From Pull Request To Patient Safety: How Tidepool Built an Open-Source Quality Management System - Tapani Otala, Tidepool

From Pull Request To Patient Safety: How Tidepool Built an Open-Source Quality Management System

By Blog, Critical Software Summit, Safety-Critical Software Summit

Open Source Summit North America 2026 and Embedded Linux Conference brought together the open source community in Minneapolis from May 18–20, 2026.

According to the event report, the event welcomed 1,231 attendees from 524 organizations, with 68% of attendees in technical positions. The program included 210 conference talks selected from 977 talks submitted, reflecting strong interest and participation across the open source ecosystem.

For the ELISA Project community, the event was an important opportunity to continue the conversation around safety-critical software, open source safety standards, regulatory compliance, requirements traceability, verification, software supply chains, and safety engineering.

The Safety-Critical Software Track highlighted practical work across several domains, including aerospace, embedded systems, medical devices, robotics, avionics, automotive, and industrial systems. Sessions explored how open source communities are addressing the technical, process, and compliance needs of safety-critical systems.

Over the next few weeks, we will highlight selected session recordings from the track and share key takeaways with the community.

Session Highlight: From Pull Request To Patient Safety: How Tidepool Built an Open-Source Quality Management System – Tapani Otala, Tidepool

In this session, Tapani Otala of Tidepool shared how Tidepool built an open source Quality Management System (QMS) for safety-critical medical software.

Tidepool is a nonprofit organization founded by people with diabetes, parents of children with diabetes, and clinicians. The organization builds open source tools for diabetes care, including Tidepool Loop, an automated insulin delivery system. Tidepool Loop uses data from a continuous glucose monitor, runs an algorithm on a phone, and communicates with an insulin pump to adjust insulin delivery. Because the software can influence insulin delivery every five minutes, including while a person is asleep, the system must be developed with strong safety and regulatory controls.

A central point of the talk was that open source and FDA-cleared medical software can coexist. Tidepool Loop was cleared by the FDA as Class II Software as a Medical Device, while the source code remained open. Tapani explained that safety and regulatory standards define what evidence and controls are needed, but they do not require the software to be closed source.

The session outlined the core elements of a QMS, including traceability, verification and validation, risk management, and change control. Tapani described QMS as a controlled, repeatable, and auditable system made up of policies, procedures, records, requirements, risks, tests, reviews, and change history.

A major part of the talk focused on how Tidepool connects engineering work to regulatory evidence. Requirements are tracked in Jira and linked to design, implementation, tests, risks, mitigations, bugs, and other records. These links are not just references; they form the structure that allows Tidepool to trace a requirement through development and testing, and then trace code or test evidence back to the original requirement.

Tapani used a specific requirement for insulin delivery presets as an example. A feature that may appear simple to users can generate a large set of safety and regulatory artifacts, including development tickets, test tickets, risk records, mitigations, UX design work, usability testing, and training requirements. In one example, a requirement for presets was connected to multiple risks and tests, showing how safety-critical software features can create significant downstream evidence needs.

The session also explained how Tidepool generates regulatory outputs from its development data. Instead of manually creating traceability matrices and risk analysis documents after development, Tidepool uses scripts to pull structured information from Jira and generate workbooks for regulatory review. These outputs include traceability views, risk analysis, hazard analysis, cybersecurity hazard analysis, and related summaries. This helps reduce manual drift and keeps documentation connected to the engineering work.

Another important topic was Tidepool’s relationship with the upstream open source Loop community. Tidepool Loop was based on the earlier do-it-yourself Loop project, which was created by a community of people who wanted better automated insulin delivery tools. Tidepool needed to maintain regulatory control over its FDA-cleared product while still staying connected to upstream innovation. The team does this by selectively bringing in changes, running them through the regulatory process, keeping shared code modular, and offering improvements back to the open source community where appropriate.

Tapani also shared lessons learned from building this system. One lesson was that the schema behind tools like Jira matters because issue types, link types, required fields, and relationships become part of the regulatory structure. Another lesson was that heavy workflow gates can slow engineers down, while downstream validation and automated checks can help maintain data quality with less friction.

The broader takeaway for safety-critical open source communities is that transparency can support trust. Tidepool’s experience shows that open source development, regulatory compliance, and safety engineering can work together when traceability, risk management, testing, and change control are built into the development process.

As safety-critical software continues to expand across medical, automotive, aerospace, industrial, and embedded systems, Tidepool’s work offers a practical example of how open source communities can build auditable processes while keeping development open and collaborative.

Watch the session recording here.

Stay tuned for more Safety-Critical Software Track session highlights from Open Source Summit North America 2026. Check the playlist here.

Session Clip - ELISA Seminar – AvioNix: Infrastructure as Code for Linux in Avionics

How AvioNix Supports Reproducibility and Traceability for Linux in Avionics

By Blog, Seminar Series

The ELISA Project hosted a seminar on AvioNix: Infrastructure as Code for Linux in Avionics, featuring Wanja Zaeske, Research Scientist at the German Aerospace Center, and Erin Vanderveen, Sr. Specialist Functional Engineer at Tweag by Modus Create.

The session focused on a key challenge for bringing Linux into safety-critical aviation applications: open source software is distributed and released in many different ways. Compared to COTS walled-garden safety-critical operating systems, this diversity can create long “getting started” processes, “works on my machine” issues, and the need for robust SBOM tracking.

Erin began with an introduction to Nix, explaining that Nix is not one single tool, but an ecosystem that includes the Nix CLI, Nix daemon, Nix store, Nix language, Nix packages, and NixOS. The talk showed how Nix supports declarative, reproducible, and reliable builds by using explicit build inputs, isolated build environments, and unique store paths.

The session also explained how Nix can help solve common dependency and developer environment problems. With Nix, packages and development shells can be described in a way that allows contributors to enter the same build environment and reproduce the same results across machines.

Traceability was another important theme. Because Nix captures exact dependencies and build inputs, it can support detailed SBOM generation. This is especially useful for safety-critical software efforts where teams need a clear view of what components are included and how they were built.

Wanja then showed how these Nix concepts are being applied in the ELISA Aerospace Working Group through AvioNix, a Nix-based approach for building aerospace demo applications. The demonstration used the ELISA Aerospace Working Group repository and showed how contributors can build applications with a single command, compile the Linux kernel, inspect kernel configuration, and create development environments for debugging and experimentation.

The demo also showed how NixOS can be used to build a fully integrated system that includes a Linux kernel, user space, ELISA Aerospace Working Group demo applications, and a NASA cFS-based monitor. This included a light switch demo application and related monitoring software running inside a QEMU-based system.

A practical troubleshooting example highlighted how Nix can support debugging. The speakers showed how to add GDB, enable debug symbols, access the exact source used during the build, identify missing Linux kernel configuration options, and rebuild the system with the required changes.

The session also covered cross-compilation, an important topic for aerospace environments where development machines and target platforms may use different architectures. Nix provides mechanisms to describe build, host, and target platforms so teams can build software for different hardware configurations more consistently.

A key takeaway from the session was that Nix can scale across the software stack. It can support individual packages, development shells, Linux kernel builds, user space, virtual machines, and integrated system images. For the ELISA Aerospace Working Group, AvioNix provides a practical demonstrator for making Linux-based aviation software easier to build, reproduce, test, debug, and share.

The Q&A highlighted practical ways Nix can support existing engineering workflows while improving reproducibility and experimentation. One attendee asked whether it is easy to branch from an existing Nix package to explore changes. Wanja explained that this can be done by copying the expression into a project tree and modifying it, or by using Nix’s override mechanisms. Since Nix treats packages as functions, teams can create variations of a package, apply patches, or adjust build phases without rewriting the entire package definition. This is especially useful in avionics-related work, where less common architectures may require package-specific changes.

Another question focused on whether Nix can replace CMake. Wanja explained that while Nix can be used as a build system, he would not typically use it to replace CMake in a project that already uses CMake. Instead, Nix can layer around CMake by providing the required dependencies, libraries, and build environment. In the demo, the NASA cFS application still used CMake, while Nix handled the surrounding package and dependency setup.

The discussion also compared Nix with building inside a virtual machine and redistributing the VM image. Wanja noted that a VM image alone does not guarantee reproducibility. Build systems may download missing libraries, pull changing upstream branches, or install dependencies dynamically, which can lead to different results over time. With Nix, the desired system is described through Nix expressions, making the build inputs and dependencies more explicit and easier to understand than a binary VM image.

Attendees also asked how Nix compares with CMake or Bazel when starting a new product. Wanja described CMake and Nix as having different scopes: CMake builds the software, while Nix works more like a meta build system that makes the needed dependencies available. Erin added that Nix and Bazel can also be combined, including through Bazel rules that use Nix packages to provide reproducible dependencies.

At the end of the session, there was also a question about the relationship between Dhall and the Nix language. Erin explained that Dhall and the Nix language are both configuration languages, but separate tools. He also noted that Nix as a whole is more than the Nix language; it also includes the CLI, daemon, store, package collection, and NixOS.

As the community continues exploring Linux for safety-critical aviation applications, AvioNix demonstrates how Infrastructure as Code can help improve reproducibility, traceability, and collaboration across open source aerospace development. The discussion also showed that AvioNix is not about replacing existing tools such as CMake, Bazel, virtual machines, or Linux kernel workflows. Instead, it shows how Nix can provide a reproducible and traceable layer around those tools so aerospace contributors can build, debug, test, and share Linux-based demo systems more consistently.

Software Supply Chain Management With the Yocto Project - Joshua Watt, Garmin

Software Supply Chain Management With the Yocto Project – Joshua Watt, Garmin

By Blog, Critical Software Summit, Industry Conference, Safety-Critical Software Summit

Open Source Summit North America 2026 and Embedded Linux Conference brought together the open source community in Minneapolis from May 18–20, 2026.

According to the event report, the event welcomed 1,231 attendees from 524 organizations, with 68% of attendees in technical positions. The program included 210 conference talks selected from 977 talks submitted, reflecting strong interest and participation across the open source ecosystem.

For the ELISA Project community, the event was an important opportunity to continue the conversation around safety-critical software, open source safety standards, regulatory compliance, requirements traceability, verification, software supply chains, and safety engineering.

The Safety-Critical Software Track highlighted practical work across several domains, including aerospace, embedded systems, medical devices, robotics, avionics, automotive, and industrial systems. Sessions explored how open source communities are addressing the technical, process, and compliance needs of safety-critical systems.

Over the next few weeks, we will highlight selected session recordings from the track and share key takeaways with the community.

Session Spotlight: Software Supply Chain Management With the Yocto Project

This week, we are highlighting Software Supply Chain Management With the Yocto Project by Joshua Watt, Garmin.

Managing software supply chains is an important part of safety-critical software. In this session, Joshua described the technologies, methods, and lessons learned that the embedded software space uses to manage software supply chains with the Yocto Project.

The talk began with a core supply chain question: what is inside the binaries being shipped, and can those binaries be traced back to the source code that produced them? Joshua explained that teams need visibility into software versions, origin, licenses, possible tampering, vulnerabilities, and the build infrastructure used to produce final outputs.

Joshua also discussed the role of SBOMs. While the session was not primarily about SBOMs, he explained how SBOMs provide visibility into the software supply chain and offer a standardized format for sharing information with customers, regulators, internal teams, and other stakeholders.

The session then introduced the OpenEmbedded and Yocto Project build flow. Joshua explained the relationship between OpenEmbedded, BitBake, and the Yocto Project, and showed how source code, recipe metadata, and policy information are processed to produce target images, packages, SDKs, firmware, containers, package feeds, and build tools.

A key point in the talk was how BitBake tracks dependencies using task hashes. These hashes connect build inputs, recipe metadata, source code, native tools, cross compilers, target packages, and final images. Because of this, the Yocto Project has a strong link between the software output and the inputs that produced it.

Joshua explained how this information is expressed through SPDX documents generated during the build and merged into a final SBOM. These SBOMs can include runtime dependencies, build-time dependencies, native tools, cross compilers, source files, package outputs, and other build information that the Yocto Project directly knows from its metadata and build process.

The talk also covered static library tracking. Static libraries can be difficult to identify after they are linked into an application, but because the Yocto Project builds from source and can use debug information, it can connect applications back to the static libraries, recipes, and source code that produced them.

Another major topic was reproducible builds. Joshua explained why reproducibility matters for supply chain management, including detecting unexpected changes, identifying possible tampering, improving quality assurance, supporting delta updates, and avoiding unnecessary rebuilds. He also described how the Yocto Project autobuilder tests reproducibility across package formats and host distributions, while encouraging teams to test reproducibility in their own configurations.

The session closed by looking at the build tools tarball, which can replace many host tools and extend supply chain traceability into the build infrastructure itself. Joshua described how this can help teams trace target images back through the tools used to build them and, potentially, to a known trusted host.

For safety-critical software, this session reinforced that supply chain management is about more than producing a list of components. It is about understanding how software is built, where it comes from, what it depends on, and how confidently teams can trace final binaries back to their sources and build process.

Watch the session recording here.

Stay tuned for more Safety-Critical Software Track session highlights from Open Source Summit North America 2026. Check the playlist here.

Modernizing Software Verification - Craig Christianson, United States Air Force

Modernizing Software Verification – Craig Christianson, United States Air Force

By Blog, Critical Software Summit, Industry Conference, Safety-Critical Software Summit

Open Source Summit North America 2026 and Embedded Linux Conference brought together the open source community in Minneapolis from May 18–20, 2026.

According to the event report, the event welcomed 1,231 attendees from 524 organizations, with 68% of attendees in technical positions. The program included 210 conference talks selected from 977 talks submitted, reflecting strong interest and participation across the open source ecosystem.

For the ELISA Project community, the event was an important opportunity to continue the conversation around safety-critical software, open source safety standards, regulatory compliance, requirements traceability, verification, software supply chains, and safety engineering.

The Safety-Critical Software Track highlighted practical work across several domains, including aerospace, embedded systems, medical devices, robotics, avionics, automotive, and industrial systems. Sessions explored how open source communities are addressing the technical, process, and compliance needs of safety-critical systems.

Over the next few weeks, we will highlight selected session recordings from the track and share key takeaways with the community.

Session Spotlight: Modernizing Software Verification

This week, we are highlighting Modernizing Software Verification by Craig Christianson, United States Air Force.

Craig opened the session by discussing the difference between “software craftsmanship” and “software engineering,” using the analogy of building structures to explain why safety-critical software needs more than trial, error, and confidence. When software can affect whether people are protected or put at risk, stronger assurance practices are needed.

The session shared real-world examples of software in safety-critical contexts, including systems where software can help protect lives and systems where failure or compromise could create serious risk. Craig also discussed the compliance challenges faced by software engineers working on safety-critical software, including the rigorous and time-consuming nature of assurance and certification processes.

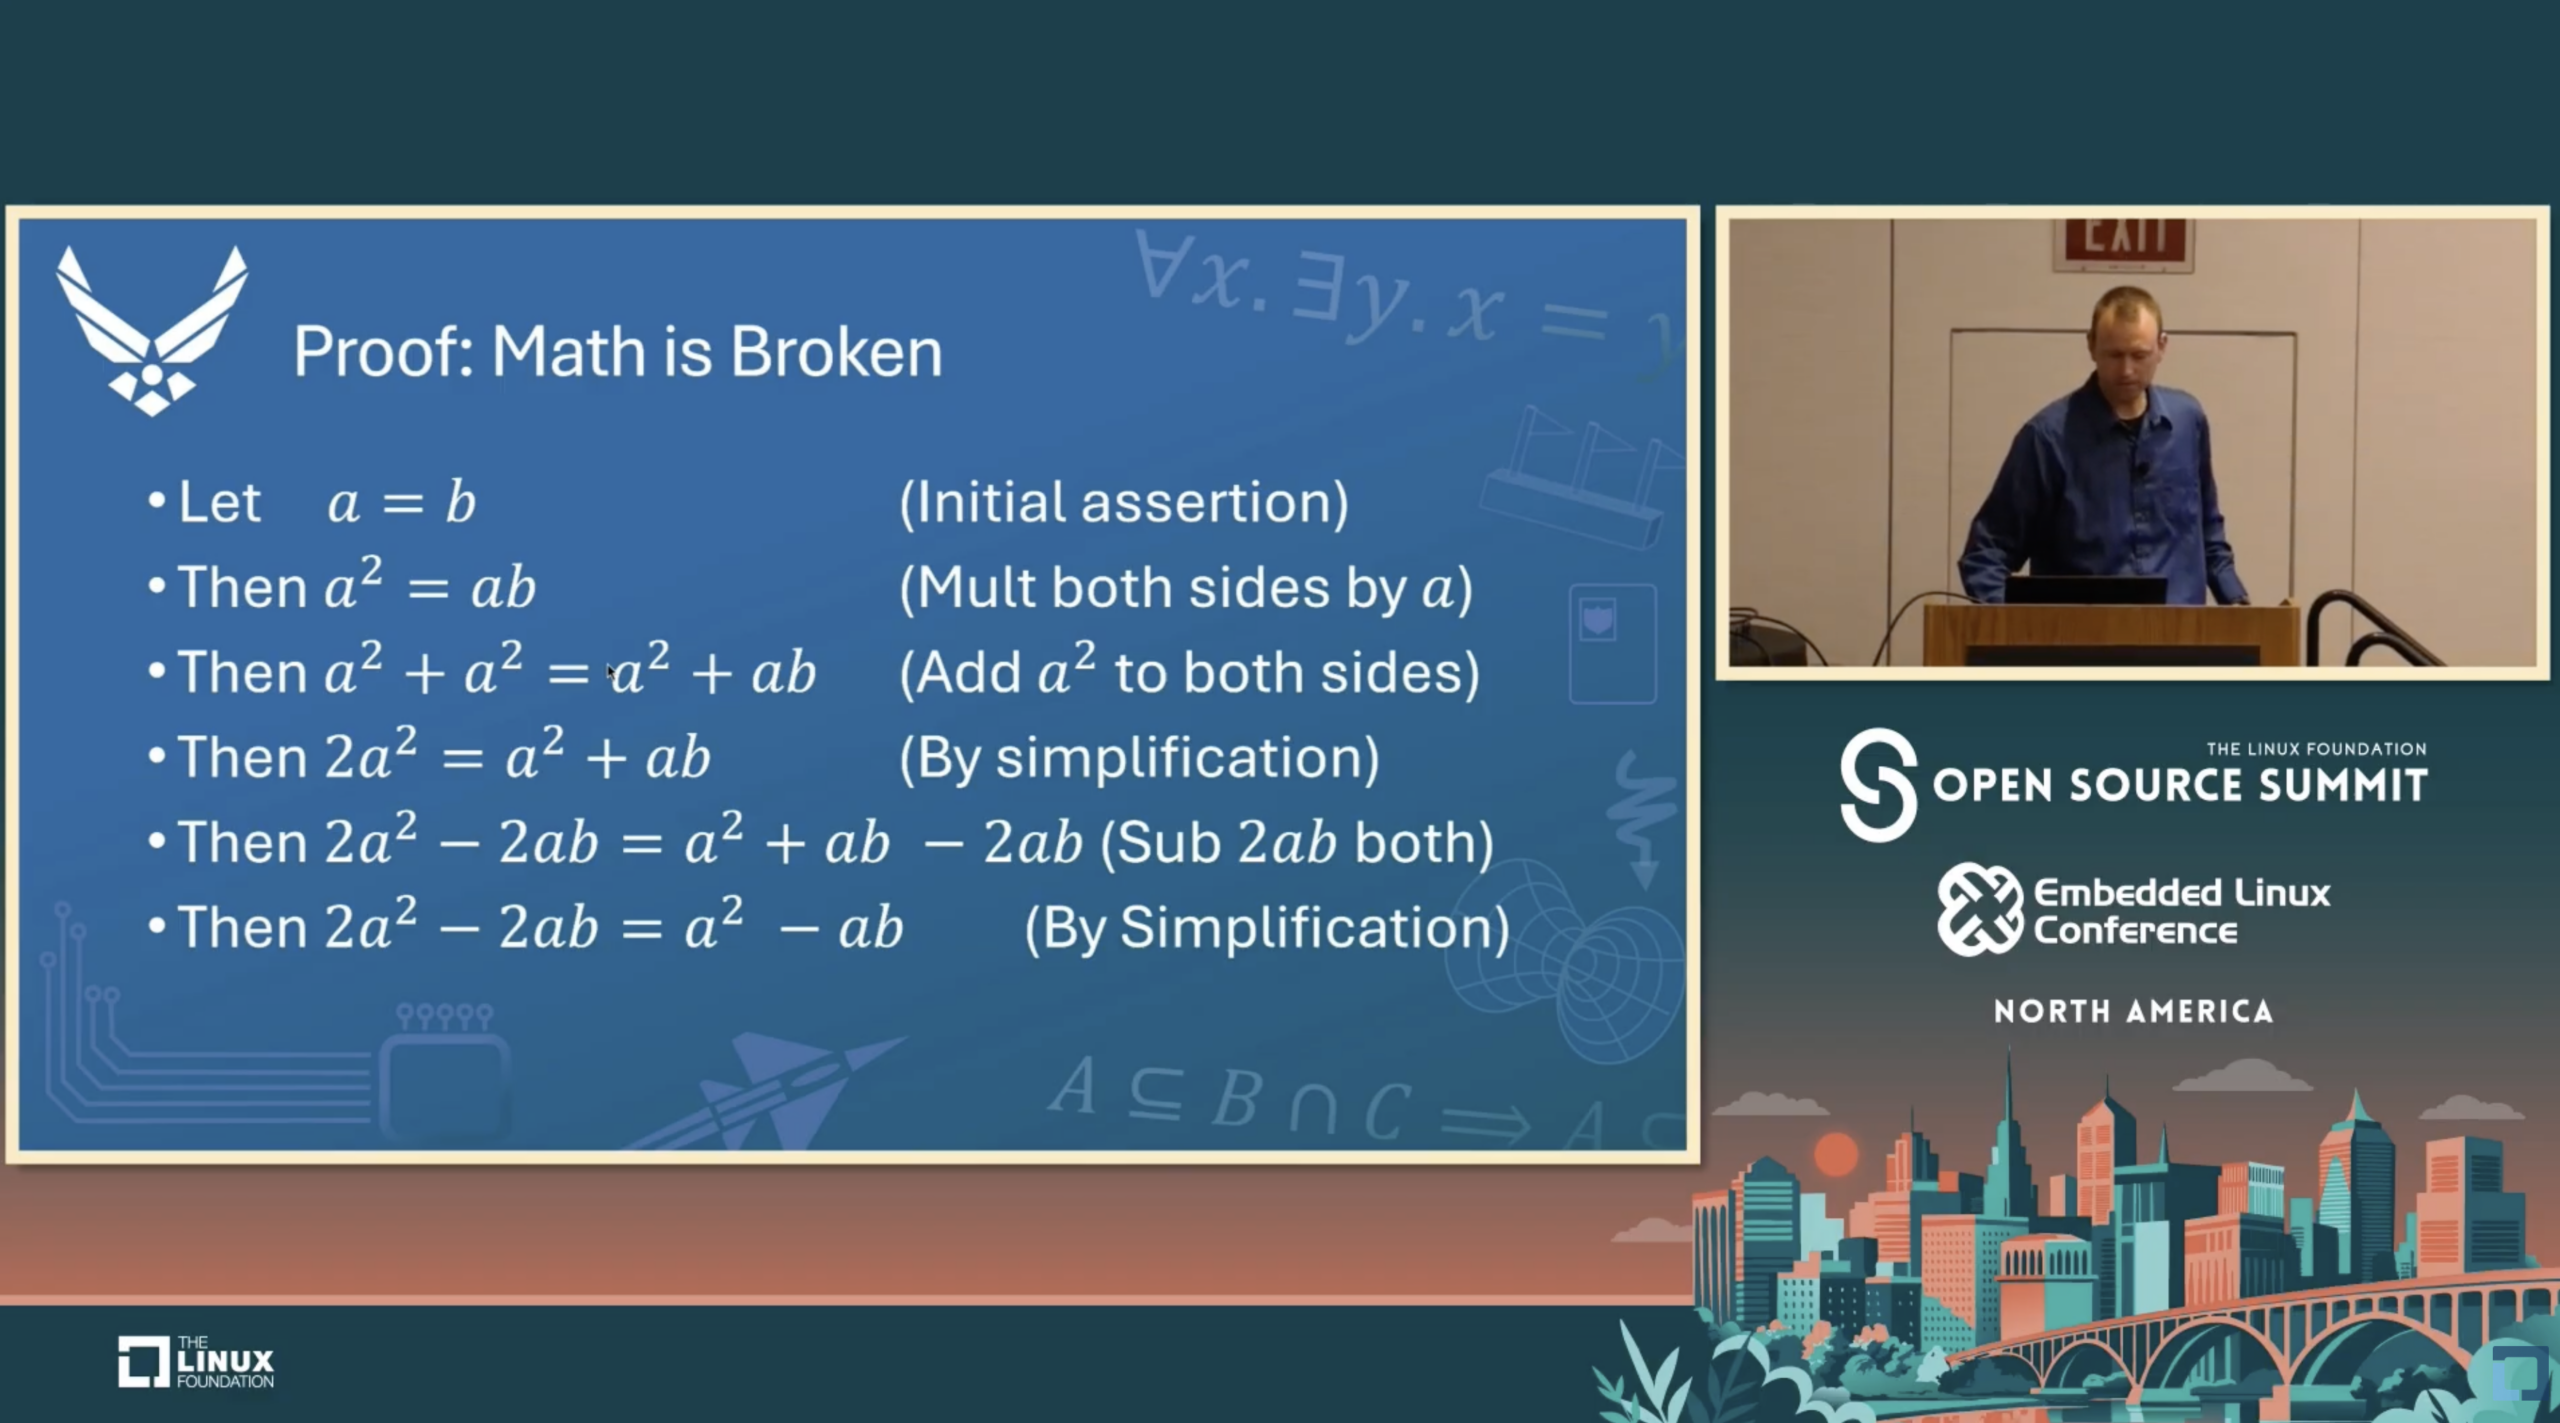
A key part of the talk focused on software assurance and the role of traceability across requirements, specifications, design, implementation, and maintenance. Craig explained how traditional assurance often depends on systematic evaluation, testing, reviews, and evidence, while formal verification uses mathematical models and proofs to reason about system behavior.

The session then explored how automated reasoning can help improve formal methods by making proofs machine-checkable, repeatable, reusable, and less dependent on manual human reasoning. Craig introduced automated reasoning tools and semantics, and showed how these approaches can help reduce errors in logical reasoning.

Craig also discussed the seL4 microkernel as an example of a system supported by formal verification. The talk explained how a small trusted computing base, strong isolation, and publicly available proofs can support higher assurance, while also noting that formal methods still rely on clearly stated assumptions.

The session concluded with a practical demonstration project built for seL4 using the Microkit build system. Craig walked through a Raspberry Pi example, showing how protection domains, mapped device registers, notifications, and hardware interrupts can be used to build a simple system while reasoning more carefully about separation and system behavior.

As open source continues to expand into regulated and safety-critical domains, this talk highlighted why modern verification methods matter. Formal methods and automated reasoning are not a replacement for all testing, but they can help strengthen assurance, improve traceability, reduce certain classes of errors, and support safer systems over time.

Watch the session recording here.

Stay tuned for more Safety-Critical Software Track session highlights from Open Source Summit North America 2026. Check the playlist here.

ELISA Project at Open Source Summit North America 2026

Recap: ELISA Project at Open Source Summit North America 2026

By Ambassadors, Blog, Safety-Critical Software Summit

Open Source Summit North America 2026 brought together developers, contributors, maintainers, technologists, and community leaders to share knowledge, collaborate on solutions, and push open source projects forward.

The ELISA Project participated in the Safety Critical Software Track, which explored the intersection of open source and safety standards. Sessions covered best practices for regulatory compliance, security updates, safety engineering, requirements traceability, quality assessments, safety analysis methodologies, and technical development for safety-critical systems.

The track featured sessions on Space Grade Linux graduating from ELISA incubation, software supply chain management with the Yocto Project, Xen’s path toward safety certification, Tidepool’s open source quality management system for patient safety, deterministic interoperability in medical robotics, and modern approaches to software verification.

Together, these sessions highlighted how open source communities are advancing practical approaches for building reliable, transparent, and safety-critical systems across industries including aerospace, embedded systems, medical devices, robotics, and critical infrastructure.

The session playlist is now available. Watch the recordings here.

Thank you to all speakers, attendees, contributors, and community members who joined the conversations and continue to support the advancement of open source in safety-critical software.

ELISA project at Open source summit

ELISA Project Momentum Continues: Join Us at Upcoming Workshops, Safety Track Sessions, and Open Source Events

By Blog, ELISA Summit, Industry Conference, Safety-Critical Software Summit, Workshop

The ELISA Project continues to grow as the open source ecosystem increasingly recognizes the importance of safety-critical systems, embedded Linux, requirements traceability, and collaborative safety engineering. Across industries such as automotive, aerospace, industrial, medical, rail, and energy, Linux is playing a larger role in systems where dependability, transparency, and long-term maintainability matter.

As this momentum builds, ELISA is expanding its presence across key open source events in 2026, creating more opportunities for contributors, maintainers, safety experts, developers, and industry leaders to collaborate.

Whether you are already involved in safety-critical Linux or are just beginning to explore how open source can support safety engineering, these upcoming events are great opportunities to learn, contribute, and connect with the ELISA community.

ELISA Workshop London 2026

The next ELISA Workshop will take place June 9–11, 2026, in London, co-hosted with Canonical. The workshop will gather ELISA members, contributors, and ecosystem partners for in-person collaboration, technical discussions, and planning around the project’s next steps. Register for the workshop here.

The London workshop agenda reflects the growing breadth of ELISA’s work. Sessions will explore safety-critical Linux, cybersecurity compliance, PREEMPT_RT latency monitoring, AI-based tooling for safety-critical development, SPDX modeling for safety cases, Software Heritage identifiers, kernel test coverage, safety manuals, Linux kernel requirements, and industry approaches to qualified Linux.

This workshop is an important opportunity for the community to collaborate directly, share progress, discuss challenges, and help define what comes next for safety-critical Linux.

Don’t miss it: registration is required, and seats are limited for in-person attendance.

Open Source Summit 2026 – Mumbai, India

ELISA’s work also connects naturally with the broader conversations happening at Open Source Summit 2026 – Mumbai, India, taking place June 16–17, 2026.

Open Source Summit is a key gathering place for developers, maintainers, technologists, community leaders, OSPO teams, legal experts, policy advocates, standards organizations, and open source ecosystem leaders. It is where the full spectrum of open source communities come together, from Linux and embedded systems to AI, cloud infrastructure, DevOps, security, and safety-critical systems.

The Mumbai event will include tracks such as Embedded, Linux, Linux for Emerging Countries, Open AI & Data, OSS Enabling & Management, Security-adjacent ecosystem topics, Zephyr, and more. For the ELISA community, this is a valuable opportunity to connect safety-critical systems work with adjacent open source domains including embedded Linux, long-term maintenance, security, and ecosystem sustainability.

Open Source Summit 2026 – Seoul, Korea

The momentum continues at Open Source Summit 2026 – Seoul, Korea, taking place August 11–12, 2026.

Like other Open Source Summit events, the Seoul gathering will bring together the technical and non-technical leaders shaping open source. It will provide another important forum for conversations around open source collaboration, governance, safety, security, sustainability, and the role of Linux across industries.

The schedule is expected to go live on June 11, 2026, making this a good time for the ELISA community to watch for relevant sessions, plan participation, and encourage colleagues across the safety-critical and embedded systems ecosystem to attend.

Open Source Summit Europe 2026: Submit Your CFP

ELISA is also encouraging community members to submit proposals for Embedded Linux Conference & Open Source Summit Europe 2026, taking place October 7–9, 2026.

This is a major opportunity to share real-world work, lessons learned, and technical progress related to safety-critical and embedded Linux systems. Suggested submission topics include:

Safety-critical software, open source and safety standards, working with regulatory authorities, security updates for safety-critical systems, safety engineering in open source projects, development data and quality assessment, requirements traceability and testability, safety analysis methodologies, safety-relevant technical features, and case studies from aerospace, automotive, industrial, medical, energy, and other safety-critical domains.

Important dates:

CFP closes: Wednesday, June 24, 2026, at 23:59 CEST
CFP notifications: Friday, July 24, 2026
Schedule announcement: Wednesday, July 29, 2026
Event dates: Wednesday, October 7 – Friday, October 9, 2026

Whether you are working on kernel requirements, safety cases, testing, tooling, compliance, documentation, traceability, or real-world deployment, your experience can help move the ecosystem forward.

ELISA at Linux Plumbers Conference 2026: Safe Systems with Linux Microconference

ELISA will also be part of the Safe Systems with Linux Microconference at Linux Plumbers Conference 2026, taking place October 5–7, 2026, at the Prague Congress Centre in Prague, Czechia, with hybrid participation available.

As Linux is increasingly used in systems with varying levels of criticality, the need for traceability between requirements, code, tests, and supporting artifacts is becoming more urgent. The Safe Systems with Linux Microconference will focus on how the Linux kernel ecosystem can better support structured requirements, documentation, testing, and artifact sharing while preserving the flexibility and speed of upstream development.

This year’s discussion will build on prior work around expressing requirements and traceability as sidecar data structures. Topics will include requirements-driven testing, semantic aspects of kernel requirements, the Linux Kernel Requirements Framework, automation tooling, technical debt reduction, kernel quality initiatives, industry adoption, and the role of requirements in education and onboarding.

The microconference is an excellent place for kernel developers, maintainers, safety architects, tooling experts, and industry stakeholders to collaborate on practical approaches for dependable, safety-relevant systems with Linux.

Why This Matters

The ELISA Project is growing because the need is growing.

Industries want to use Linux and open source software in systems where reliability, accountability, and safety evidence matter. At the same time, open source communities need approaches that respect upstream development practices rather than forcing traditional safety processes into workflows where they do not fit.

ELISA helps bridge that gap.

By bringing together experts from across organizations and industries, ELISA supports shared methods, common terminology, reusable evidence, stronger tooling, and open collaboration around safety-critical Linux. The project’s involvement in workshops, Open Source Summit events, and safety-focused sessions reflects a broader shift: safety-critical open source is no longer a niche conversation. It is becoming a central part of the open source ecosystem.

Get Involved

Now is the time to participate.

Attend the ELISA Workshop in London. Join the conversations at Open Source Summit India, Korea, and Europe. Submit a CFP for Open Source Summit Europe. Take part in the Safe Systems with Linux Microconference at Linux Plumbers Conference. Share your use cases, your challenges, your tools, and your lessons learned.

The future of safety-critical systems with Linux will be built through collaboration, and ELISA is helping create the space for that work to happen.

ELISA Seminar – Functional safety with Xen, Zephyr and Linux for avionics, automotive and industrial

Recap – ELISA Seminar – Functional safety with Xen, Zephyr and Linux for avionics, automotive and industrial

By Ambassadors, Blog, Seminar Series, Technical Update, Working Group

On May 13, 2026, the ELISA Project hosted a seminar exploring how open source technologies including Xen, Zephyr RTOS, and Linux are advancing toward deployment in safety-critical systems across avionics, automotive, and industrial domains.

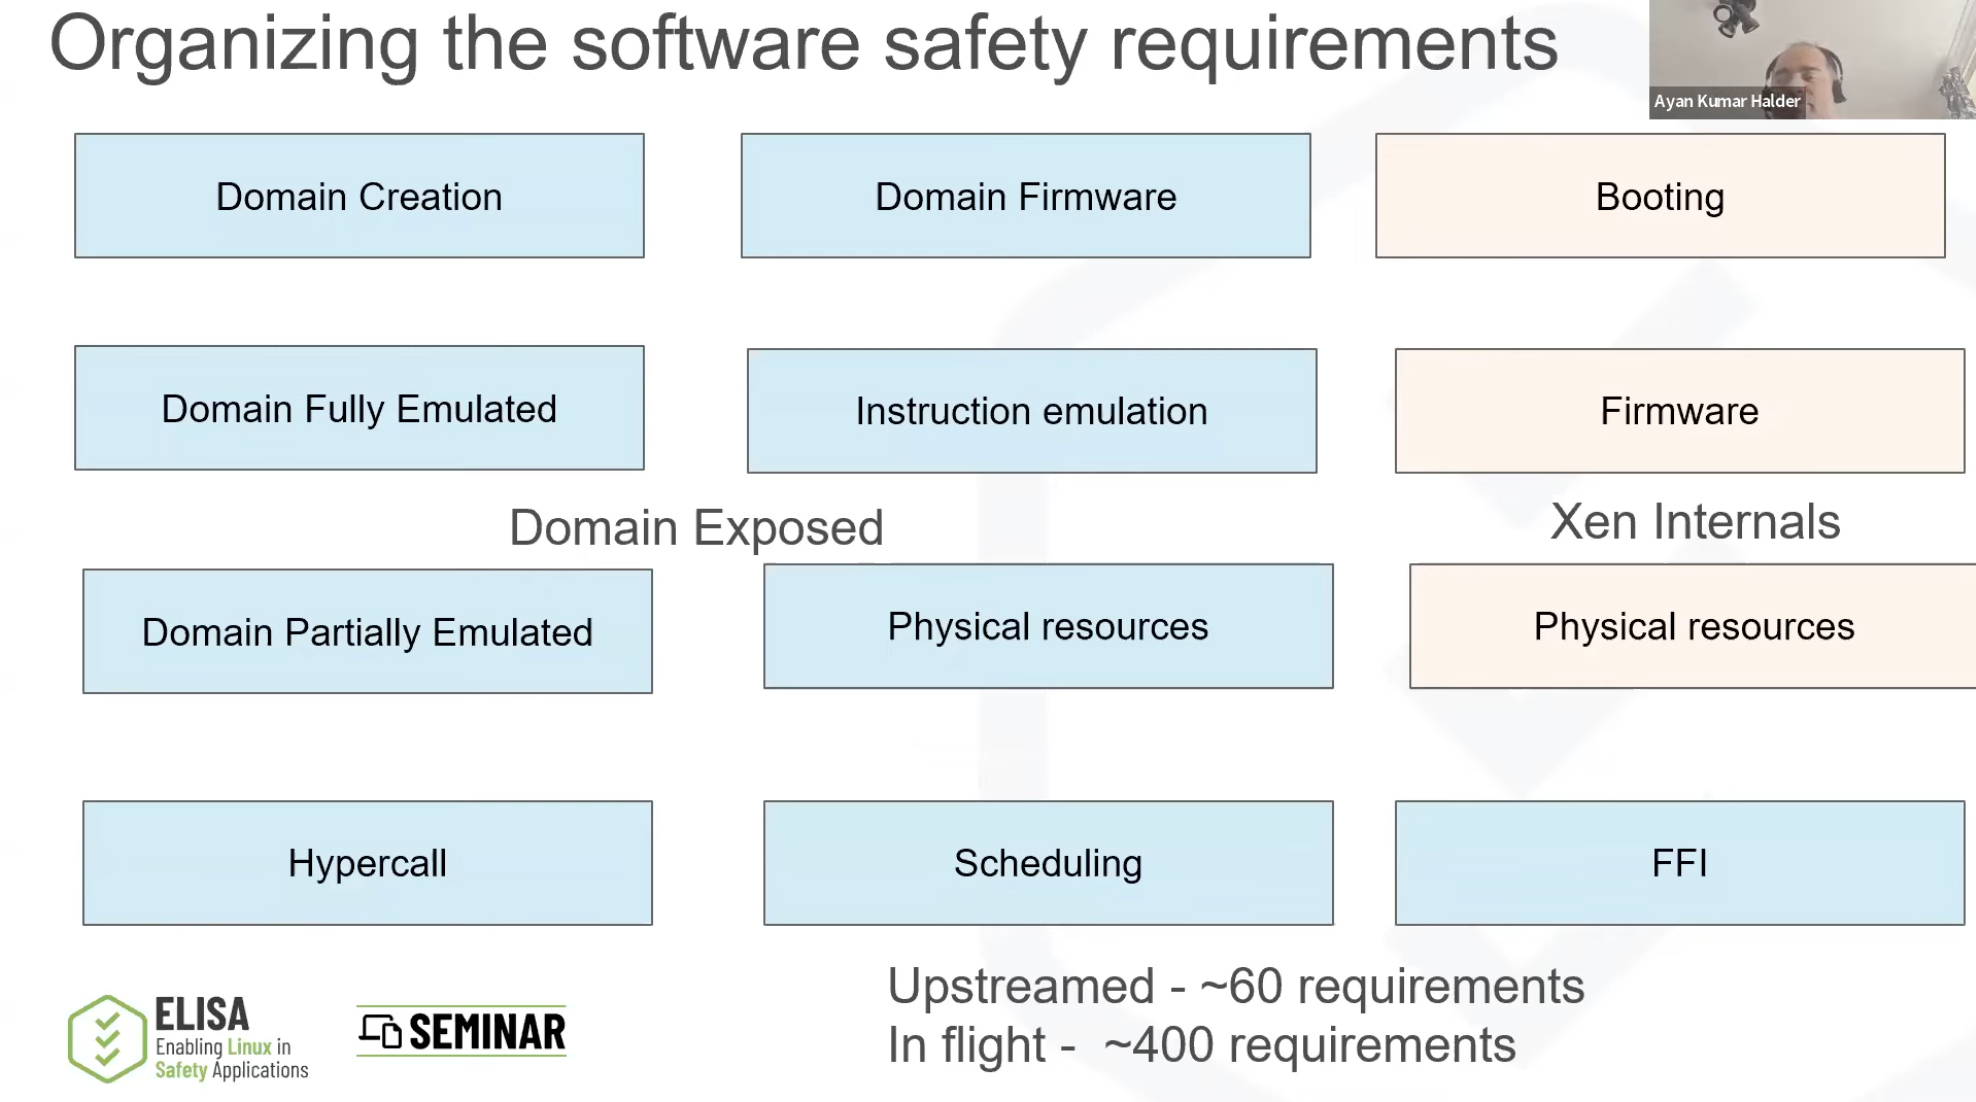
The session featured Ayan Kumar Halder (AMD) and Matthew Weber (Boeing), who shared ongoing collaborative work around functional safety, mixed-criticality systems, and open source safety certification efforts.

The discussion focused on how Xen, Zephyr, and Linux can be composed into a unified architecture for safety-critical environments. The speakers outlined how Xen can act as a Type-1 hypervisor, isolating workloads with different safety requirements while supporting deterministic execution, static partitioning, and freedom from interference between virtual machines.

A major theme throughout the session was the growing collaboration between the Xen community and the ELISA Project to build an open functional safety ecosystem. The work spans multiple safety standards including ISO 26262, IEC 61508, and DO-178C, with the goal of creating reusable safety certification artifacts and methodologies that can benefit multiple industries.

The seminar highlighted several ongoing technical efforts within the Xen functional safety initiative, including:

  • MISRA C compliance improvements and automated CI checking
  • MPU support for ARM Cortex-R systems
  • Static partitioning and deterministic scheduling
  • Requirements traceability and architecture specifications
  • Domain-based testing, fault injection, fuzzing, and unit testing
  • White-box testing approaches using Ceedling and coverage analysis
  • Open source traceability workflows using Open Fast Trace

The speakers also discussed the importance of defining assumptions of use (AoU) between system components such as firmware, hypervisors, operating systems, and applications. This systems-level perspective is critical for enabling Linux and Xen to operate within certified safety environments.

Matthew Weber shared additional insights from the aerospace domain, explaining how avionics standards such as DO-178C and ARINC 653 complement ongoing automotive safety efforts. The session explored how higher levels of testing rigor, deterministic partitioning, and lifecycle traceability can help support mixed-criticality aerospace systems using open source technologies.

Another key discussion point was sustainability. Functional safety is not a one-time activity but an ongoing engineering process that must evolve alongside code changes, new features, and emerging defects. The speakers emphasized the importance of open collaboration, transparent development processes, and community participation to keep safety-related artifacts and testing continuously maintained.

The session concluded with an invitation for the broader community to get involved through mailing lists, workshops, Git repositories, and upcoming events including the Xen Summit and ELISA workshops.

As open source continues expanding into regulated and safety-critical industries, collaborations like these are helping create the technical foundations, tooling, and community processes needed to support the next generation of safety-focused systems.

Watch for upcoming ELISA seminars and community workshops to continue the conversation around functional safety, mixed-criticality systems, and open source collaboration.

Upcoming ELISA Seminars: